Docker Commits Sandbox Kit Spec to CNCF for Neutral Governance
Docker published an open specification for packaging artificial intelligence agents and their access permissions under the Apache 2.0 license, and committed to contributing the format to the Cloud Native Computing Foundation for neutral governance, according to linux.com.
The Tech TL;DR:
- Docker released the Sandbox Kit Spec to let developers package AI agents, tools, and permission limits into a single OCI container image.
- The specification uses standard Open Container Initiative image manifest annotations to make agent authority portable across different runtimes.
- Kits for tools from companies including AWS, Box, Datadog, Dynatrace, JFrog, NanoClaw, OpenClaw, Palo Alto Networks, and Snyk are available now.
Packaging AI Agents Inside Open Container Initiative Images
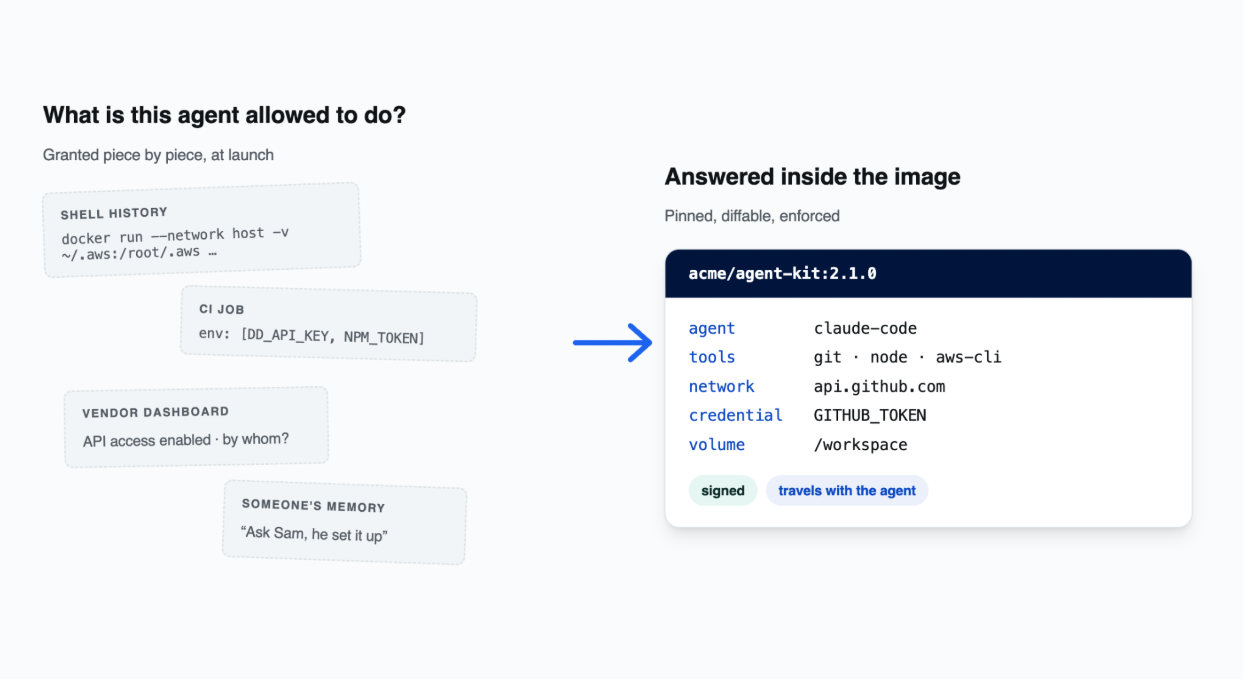
The newly published Sandbox Kit Spec addresses a growing operational gap in software engineering workflows. Standard Open Container Initiative container images instruct runtimes on how to build and start applications, but they lack native mechanisms to designate permitted network hosts, specific credentials, or persistent file volumes. For traditional web services, runtime access parameters were typically managed outside the image via docker run flags or Compose files. AI coding assistants such as Claude Code and Codex dynamically determine execution paths at runtime, requesting package installations and API access piece by piece to complete tasks.
Because these permissions accumulate informally over time across shell histories and configuration dashboards, engineering teams frequently struggle to audit exact agent privileges. The Sandbox Kit Spec embeds a typed capability list directly inside an ordinary OCI container image manifest using existing annotation extension points. By using current registry, scanning, and signing tools without requiring modifications to underlying infrastructure, the specification binds an agent directly to its designated operational boundaries.
Linux Foundation Governance Prevents Vendor Lock-In for Sandbox Kits
Chris Aniszczyk, CTO of the CNCF, stated that standards allow ecosystems to move fast without fragmenting, noting that delivering Sandbox Kits as standard OCI images provides an open and repeatable way to package agents and guardrails together. Docker originally deployed Kits as a core feature of Docker Sandboxes, running agents within isolated microVMs to enforce specific boundary limits. Moving the specification under Linux Foundation governance is intended to ensure that any conforming runtime can implement the format rather than locking developers into a single vendor ecosystem.
With availability spanning multiple enterprise technology stacks, platform teams can now publish standardized Kits across corporate environments. Developers can pull identical agent images accompanied by verified permission constraints, review modifications through standard image diff tools, and prevent unauthorized privilege escalation before execution.
# Build and inspect a Sandbox Kit OCI image manifest
docker build -t my-secure-agent:v1 .
docker inspect my-secure-agent:v1
Implementation Workflows for Enterprise Development Teams
When an agent requests broader resource access in a subsequent version update, the modification registers as explicit lines added to the image manifest that reviewers can actively reject. This artifact-driven authority model ensures that security policies travel with the code artifact rather than remaining trapped in scattered documentation.
Disclaimer: The technical analyses and security protocols detailed in this article are for informational purposes only. Always consult with certified IT and cybersecurity professionals before altering enterprise networks or handling sensitive data.