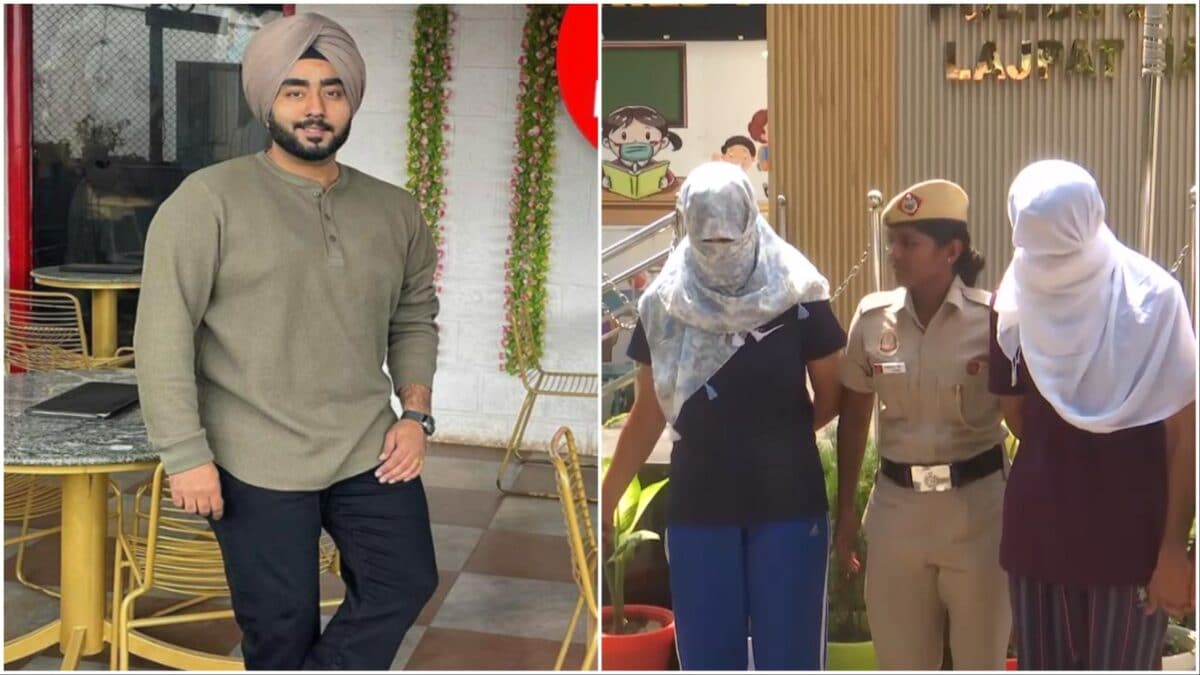
Sell Your Wife WhatsApp Message Surfaces in Rs 1.2 Crore Fraud Linked to Yuvraj Manchanda Murder Case
Forensic Analysis: Digital Artifacts and Encryption Layers in the Yuvraj Manchanda Murder Case
A chilling WhatsApp message containing the phrase “sell your wife, do anything” has surfaced in connection with an alleged Rs 1.2 crore fraud case linked to the accused in the Yuvraj Manchanda murder investigation. According to initial police disclosures and digital forensic reviews, the recovered chat logs serve as a focal point for investigators tracking the financial coercion, extortion patterns, and digital footprints preceding the homicide.
The Tech TL;DR:
- Digital Evidence Recovery: Investigators extracted encrypted messaging artifacts directly from seized mobile devices, highlighting ongoing challenges in parsing proprietary application databases without master decryption keys.
- Financial Fraud Vectors: The case centers on an alleged Rs 1.2 crore monetary extraction, prompting detailed auditing of digital banking ledgers and crypto-to-fiat conversion pathways.
- IT Triage & Forensics: Corporate security teams and legal entities handling compromised communications rely on specialized digital forensic outfits like [Relevant Tech Firm/Service] to secure chain-of-custody compliance.
Decoding the Extraction: Mobile Forensics and Messaging Artifacts
Modern mobile operating systems utilize hardware-backed keystores and database encryption (such as SQLiteCipher implementations) to protect user data at rest. When law enforcement or digital investigators extract chat logs from devices associated with high-stakes criminal investigations, parsing these stores requires bypassing biometric locks, exploiting unpatched kernel vulnerabilities, or utilizing specialized Cellebrite-style hardware extraction tools. According to preliminary case records, the recovered WhatsApp communication directly ties financial duress to the broader operational timeline of the accused.
Examining chat databases on Android and iOS platforms involves reviewing SQLite journal files, write-ahead logs (WAL), and unallocated space for deleted artifacts. In scenarios where threat actors attempt to wipe application caches or purge conversation histories, forensic engineers deploy low-level block-device dumping to recover SQLite database fragments. For organizations facing internal data tampering or suspicious communications, deploying rapid response protocols through [Relevant Tech Firm/Service] ensures that volatile RAM and local storage are imaged before remote execution triggers can wipe critical logs.
Data Integrity, Chain of Custody, and Enterprise Security Audits
The convergence of physical crimes and digital fraud highlights the necessity of rigorous data integrity standards. When chat transcripts, financial transactions, and geolocation metadata are submitted as court exhibits, maintaining a cryptographic chain of custody is non-negotiable. Forensic labs generate SHA-256 hashes of every disk image immediately upon acquisition to prove that no data tampering occurred during the analysis phase.
# Generate a cryptographic hash of an acquired device image to verify integrity
sha256sum device_extracted_partition.bin > image_checksum.txt
# Verify the image against known secure boot logs
openssl dgst -sha256 -verify public_key.pem -signature signature.bin device_extracted_partition.bin
This technical rigor mirrors the compliance frameworks mandated by SOC 2 and ISO/IEC 27001 standards. Enterprises dealing with insider threats, fraudulent extortion attempts, or compromised collaboration channels cannot rely on manual log reviews. Implementing automated containerization via Kubernetes and centralized log shipping through secure pipelines helps secure sensitive endpoints against unauthorized manipulation. When vulnerabilities or unauthorized access points are identified during an internal audit, retaining [Relevant Tech Firm/Service] allows firms to execute comprehensive vulnerability assessments and patch deployment cycles seamlessly.
Future Trajectory of Digital Forensics in Criminal Investigations
As end-to-end encryption and decentralized messaging protocols become standard across consumer applications, law enforcement agencies and enterprise security operations centers (SOCs) face an expanding encrypted blind spot. The recovery of critical extortion demands in this case underscores the reality that metadata, local backup caches, and endpoint endpoint-security logs often provide the necessary breach points to reconstruct a timeline. Future iterations of digital forensic tooling will likely depend heavily on automated machine learning models capable of parsing unstructured chat data at scale, shifting the bottleneck from data collection to semantic analysis.
How do forensic investigators recover deleted chat logs from encrypted messaging apps?
What role do cryptographic hashes play in digital evidence collection?
*Disclaimer: The technical analyses and security protocols detailed in this article are for informational purposes only. Always consult with certified IT and cybersecurity professionals before altering enterprise networks or handling sensitive data.*