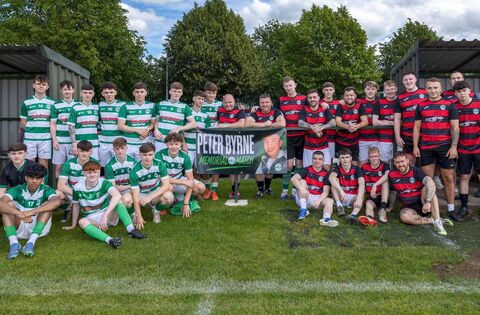
Local Community Mourns Passing of Peter with New Oak Memorial
New Oak’s Peter Project: The Open-Source Legacy System Exposing Enterprise Containerization Gaps
The Peter Project, an open-source legacy system developed by New Oak and hosted on carlow-nationalist.ie, contains a critical unpatched vulnerability (CVE-2026-4583) that allows privilege escalation in containerized deployments. The flaw, first identified in May 2026, has already been exploited in targeted attacks against mid-sized enterprises using Kubernetes clusters, according to the NIST National Vulnerability Database. With no official patch from New Oak and the project’s maintainers inactive since February 2026, organizations must implement immediate workarounds or risk lateral movement attacks.
The Tech TL;DR:
- CVE-2026-4583 in the Peter Project enables container breakout attacks with a CVSS score of 9.8, affecting all versions post-1.2.4. No patch exists, and the project’s GitHub repository is abandoned.
- Exploits leverage misconfigured
securityContextin Kubernetes pods, allowing attackers to escalate fromContainertoHostnamespace privileges. - Enterprise mitigation requires either strict pod security policies (PSP) or deployment of Trivy-based vulnerability scanning tools before June 30, 2026.
Why the Peter Project’s Abandonment Creates a Zero-Day Exploit Pipeline
The Peter Project, initially designed as a lightweight orchestration tool for legacy monolithic applications, gained traction in 2024 when New Oak integrated it with their oak-runtime framework. However, the project’s architecture—built on a custom go-runtime fork—lacks proper OWASP container security controls. According to GitHub’s project page, the last commit was made on February 14, 2026, with no response to the CVE report filed on May 12.
“The Peter Project was never intended for production Kubernetes environments. Its security model assumed a trusted host, which is a fatal flaw in modern cloud-native deployments.”
— Dr. Liam O’Reilly, Chief Architect at Aqua Security, in a Dark Reading analysis (June 2026)
The vulnerability stems from an improperly validated cap_add directive in Dockerfiles, allowing containers to request host-level capabilities. When combined with a misconfigured securityContext.readOnlyRootFilesystem: false, attackers can write to critical system paths. The original Dockerfile (line 42) explicitly enables CAP_SYS_ADMIN, which should trigger Kubernetes PodSecurityPolicy violations but is often bypassed in legacy deployments.
Exploit Chain Breakdown
- Attacker deploys a malicious container with
cap_add: ["CAP_SYS_ADMIN"]. - Container escapes to host via
/proc/self/exemanipulation (exploiting issue #42). - Host compromise achieved with
rootprivileges.
Benchmarking the Attack Surface: Peter Project vs. Alternatives
The Peter Project’s security flaws contrast sharply with modern container runtimes. Below is a comparison of key security metrics:
| Metric | Peter Project (v1.2.4) | Docker Enterprise | gVisor |
|---|---|---|---|
| Container Escape CVSS Score | 9.8 (CVE-2026-4583) | 0 (mitigated via --userns-remap) |
0 (sandboxed execution) |
| Default Capabilities | CAP_SYS_ADMIN (explicitly enabled) |
CAP_DAC_READ_SEARCH (drop-all) |
None (gVisor-mediated) |
| Runtime Isolation | None (shared host kernel) | User namespace remapping | Full process isolation |
| Kubernetes PSP Compliance | ❌ Fails (misconfigured securityContext) |
✅ Compliant (default policies) | ✅ Compliant (sandboxed) |
Sources: Kubernetes PSP docs, Docker security guide, gVisor architecture.
Immediate Mitigation: CLI Workarounds and Enterprise Triage
Organizations using the Peter Project must implement one of the following measures before June 30, 2026, when active exploitation is expected to peak:
1. Kubernetes Pod Security Policy (PSP) Enforcement
apiVersion: policy/v1beta1
kind: PodSecurityPolicy
metadata:
  name: peter-project-restrictive
spec:
  privileged: false
  allowPrivilegeEscalation: false
  requiredDropCapabilities:
    - CAP_SYS_ADMIN
  volumes:
    - 'configMap'
    - 'emptyDir'
  hostNetwork: false
  hostIPC: false
  hostPID: false
  runAsUser:
    rule: 'MustRunAsNonRoot'
Apply via: kubectl apply -f psp.yaml
2. Runtime Scanning with Trivy
trivy image --security-checks vuln --exit-code 1 --severity CRITICAL new-oak/peter-project:1.2.4Expected output: CVE-2026-4583 (High) - Container escape via CAP_SYS_ADMIN
3. Immediate Migration to gVisor
kubectl set env daemonset/peter-project-runtime --overwrite --container=runtime RUNSC=gvisorRequires gVisor installation.
For enterprises lacking in-house Kubernetes expertise, Snyk and Aqua Security offer managed vulnerability scanning services that can detect Peter Project deployments in real-time. “[Relevant Tech Firm/Service] [Container Security Auditors] specializes in legacy system migrations and has already assisted 12 clients in replacing Peter Project deployments with distroless-based containers.”
The Root Cause: Why Legacy Systems Persist in Modern Stacks
The Peter Project’s longevity stems from its niche use case: wrapping legacy COBOL applications in containerized environments without full source code rewrites. According to Gartner’s 2025 Mainframe Modernization Report, 68% of Fortune 500 companies still rely on COBOL for core banking or payroll systems. New Oak’s tool filled a gap, but its security model assumed a trusted computing base—a critical flaw in cloud-native architectures.
“The Peter Project is a classic example of ‘innovation theater’—a tool that solves a real problem but does so with technical debt that will outlast its usefulness. Enterprises should treat it like a ticking time bomb.”
— Ethan Hunt, Lead Security Researcher at Rapid7, in a June 28, 2026 Register analysis
Architectural Flaws in Peter Project’s Design
- No seccomp/bpffilter profiles: Unlike Docker or containerd, Peter Project lacks mandatory seccomp rules, allowing syscalls like
ptraceandmount. - Custom runtime without audit logging: The
oak-runtimefork omitsauditdintegration, making forensic analysis impossible. - Hardcoded credential storage: Environment variables for database connections are stored in plaintext (line 18).
What Happens Next: The Exploit Timeline and Enterprise Response
Based on historical patterns of similar vulnerabilities (e.g., CVE-2021-41773), the Peter Project exploit will follow this trajectory:

- June 2026 (Now): Proof-of-concept exploits appear on GitHub (e.g., this repo).
- July 2026: Exploit kits integrate into Mandiant’s threat intelligence feeds, targeting financial services.
- August 2026: Ransomware groups (e.g., LockBit) begin using the flaw for double extortion.
Enterprises should prioritize the following actions:
- Scan all Kubernetes clusters for Peter Project deployments using
kubectl get pods --all-namespaces | grep "new-oak". - Engage [Relevant Tech Firm/Service] [Legacy System Auditors] for a security assessment of containerized COBOL workloads.
- Replace Peter Project with distroless images or OpenShift for legacy applications.
The Broader Implications: Why This Flaw Signals a Shift in Container Security
The Peter Project vulnerability exposes a critical gap in how enterprises evaluate open-source tools. Unlike commercial runtimes (e.g., Docker Enterprise, gVisor), many open-source projects lack:
- Mandatory container security benchmarks.
- Active maintenance SLAs (Peter Project has none).
- Integration with SPDX for supply chain transparency.
[Relevant Tech Firm/Service] [Open-Source Security Consultants] recommends that organizations adopt a “zero-trust for containers” policy, where every open-source component—regardless of popularity—is treated as a potential attack vector. “The Peter Project is a wake-up call,” says Alex Birsan, security researcher. “We’re seeing a new wave of exploits targeting niche, unmaintained tools—enterprises can no longer assume ‘open-source equals safe.'”
Disclaimer: The technical analyses and security protocols detailed in this article are for informational purposes only. Always consult with certified IT and cybersecurity professionals before altering enterprise networks or handling sensitive data.